
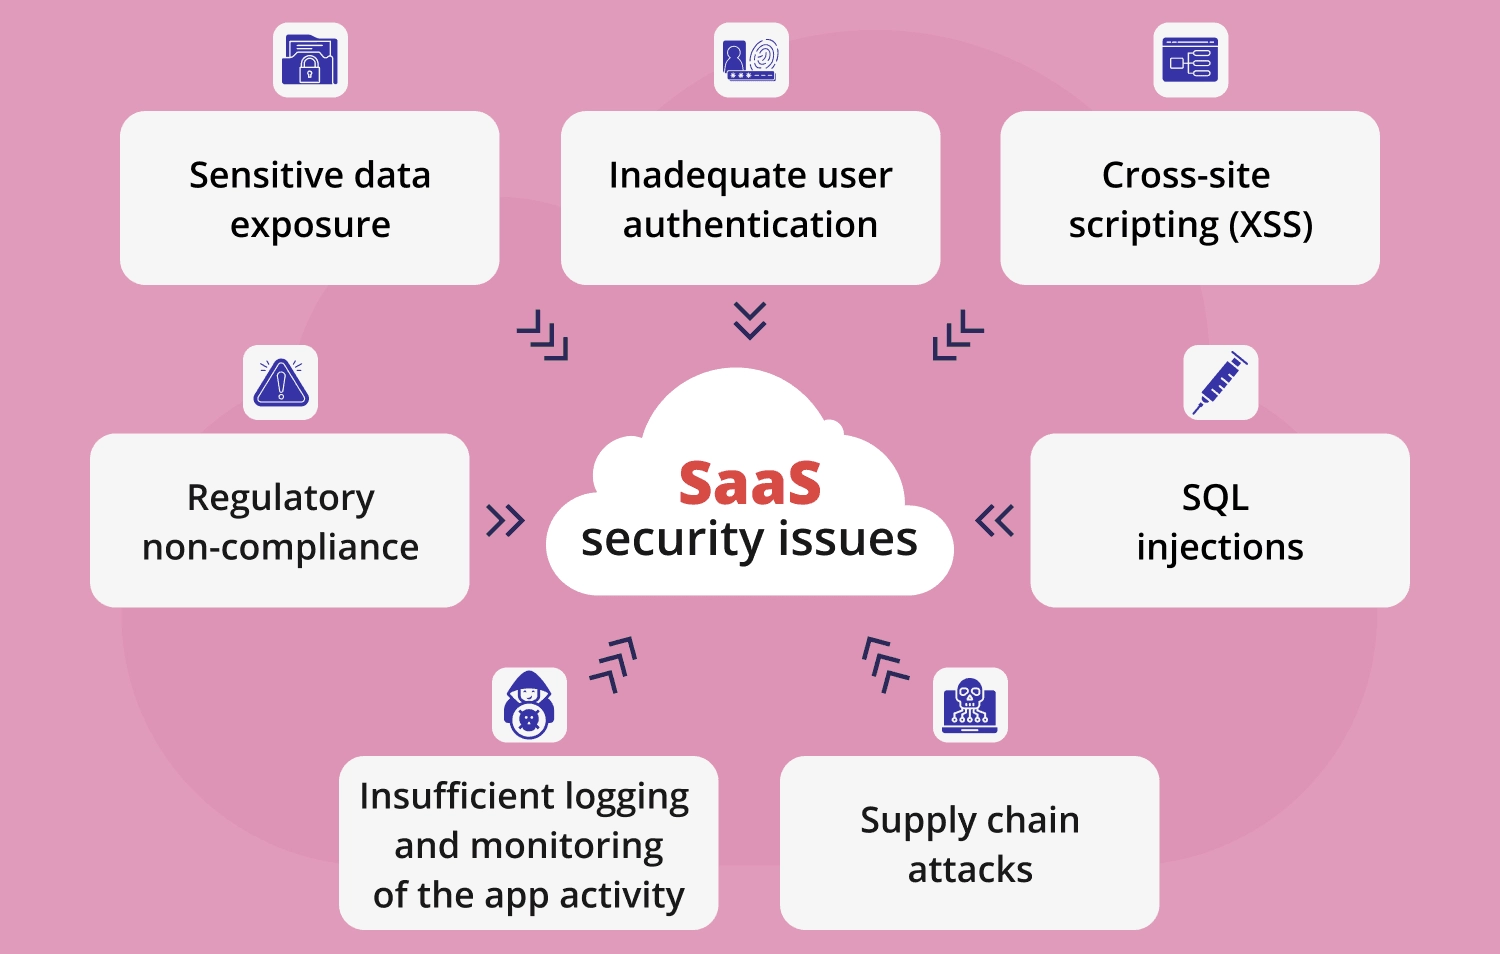
In today’s digital age, the Software as a Service (SaaS) model is rapidly becoming the backbone of operations for countless businesses. As organizations increasingly rely on SaaS applications for critical functions, the question of data security looms large. How can businesses ensure robust data security in their SaaS operations? In this comprehensive guide, we will discuss strategies, best practices, and essential considerations to include in your business plan to protect your data in a SaaS environment.
Understanding SaaS and the Importance of Data Security
SaaS refers to cloud-based software that is hosted and maintained by third-party providers. This model offers businesses flexibility, scalability, and the convenience of not managing physical infrastructure. However, with these benefits come risks, particularly concerning data security. According to the 2022 Cyber Security Breaches Survey, around 39% of businesses reported a cyber incident in the preceding year. This statistic underpins the necessity for robust data protection measures in SaaS operations.
Why Is Data Security Crucial in SaaS?
-
Sensitive Information: Many SaaS applications handle sensitive data, whether it involves customer information, financial records, or intellectual property. If this data is compromised, it can lead to severe financial losses and reputational damage.
-
Regulatory Compliance: Businesses must comply with various regulations regarding data protection, such as GDPR, HIPAA, and CCPA. Non-compliance can result in hefty fines and legal consequences.
-
Trust and Reputation: A data breach can significantly damage customer trust. Maintaining a robust data security posture helps build trust and enhances your brand reputation.
-
Business Continuity: Data breaches can disrupt business operations, causing downtime and loss of revenue. Ensuring data security is essential for maintaining business continuity.
Crafting Your Data Security Strategy in SaaS Operations
Developing a business plan that incorporates effective data security measures is vital for any organization utilizing SaaS. Below are strategic considerations for ensuring data security in your SaaS operations.
1. Assess Your Current Security Posture
Begin with a thorough audit of your existing security measures. Evaluate the policies, procedures, and technologies currently in place. Identify any vulnerabilities or gaps in your data security strategy. This initial assessment will help set the stage for enhancing your security framework.
2. Choose the Right SaaS Provider
Selecting a reputable SaaS provider is paramount. Look for providers that prioritize data security in their offerings. Key criteria to consider include:
-
Multi-Factor Authentication (MFA): Ensure the provider offers MFA to enhance access controls.
-
Data Encryption: Confirm that sensitive data is encrypted both in transit and at rest.
-
Compliance Certifications: Verify that the provider has relevant security certifications such as ISO 27001, SSAE 18, or SOC 2 compliance.
-
Incident Response Plan: Inquire about the provider’s incident response plan. A proactive approach to potential threats is crucial in mitigating risks.
3. Implement Strong Access Controls
Effective access controls are essential for safeguarding sensitive data. Here are best practices:
-
Role-Based Access Control (RBAC): Implement RBAC to limit access to data based on job roles. Ensure that employees have access only to the information necessary for their work functions.
-
Regular Access Reviews: Conduct periodic access reviews to confirm that the right individuals maintain access permissions. Revoke access for employees who have changed roles or left the organization.
-
Session Timeout Policies: Establish automatic session timeout policies to reduce the risk of unauthorized access when users are inactive.
4. Regularly Educate Employees on Security Best Practices
Human error is often the weakest link in data security. Regular training and education are essential to mitigate risks associated with employee behavior. Consider the following:
-
Phishing Awareness Training: Educate employees to recognize phishing attempts and scams. This training should include real-life examples and current tactics employed by cybercriminals.
-
Safe Password Practices: Encourage employees to use strong, unique passwords and to change them regularly. Provide resources for using password managers to simplify this process.
-
Social Engineering Awareness: Train employees on the tactics used by social engineers to manipulate individuals into revealing confidential information.

- Overcome negative thought patterns, reduce stress, and live a worry-free life
- Overthinking is the biggest cause of unhappiness
- Don't get stuck in a never-ending thought loop
- Stay present and keep your mind off things that don't matter, and never will
- Break free of your self-imposed mental prison
5. Conduct Regular Security Audits
Ongoing assessments are crucial for maintaining data security in SaaS operations. Implement a schedule for regular security audits that include:
-
Vulnerability Scans: Regularly scan your systems for vulnerabilities that cybercriminals could exploit.
-
Penetration Testing: Consider hiring third-party experts to conduct penetration testing. This proactive approach identifies weaknesses within your infrastructure.
-
Compliance Audits: Ensure ongoing compliance with regulatory requirements through regular audits.
6. Data Backup and Recovery Planning
Data loss can occur due to unexpected events, such as cyberattacks, hardware failures, or accidental deletions. Implement a robust data backup and recovery plan:
-
Regular Backups: Schedule automated backups of critical data at regular intervals. Store backups in a separate, secure location.
-
Disaster Recovery Plan: Develop a comprehensive disaster recovery plan that outlines procedures for restoring data after a breach or loss. Test the plan periodically to identify and rectify any weaknesses.
7. Monitor and Respond to Threats
Continuous monitoring is vital for identifying and responding to potential threats promptly. Implement the following measures:
-
Security Information and Event Management (SIEM): Utilize SIEM tools to monitor and analyze security events in real time. This helps detect anomalies and potential breaches.
-
Incident Response Team: Establish an incident response team responsible for acting quickly in the event of a data breach. Create clear protocols for escalation and communication during incidents.
-
Threat Intelligence: Stay informed about emerging threats and vulnerabilities in the SaaS landscape. Participate in industry forums and share intelligence with your peers.
8. Establish an Exit Strategy
As you plan for data security, consider what happens when you no longer need or wish to use a particular SaaS application. An exit strategy is essential for safeguarding your data during transitions.
-
Data Retrieval: Ensure you can retrieve your data from the SaaS provider when you choose to discontinue the service. Know the process for data extraction and obtain confirmation that all data has been returned.
-
Data Deletion: Confirm that the provider has a robust data deletion policy. After exiting the service, verify that all data has been securely deleted.
Conclusion
As the adoption of SaaS continues to grow, so too does the importance of data security. By systematically incorporating security measures into your business plan, you can mitigate risks and protect your sensitive data effectively. The strategies outlined in this guide form a solid foundation for safeguarding your SaaS operations and ensuring compliance with regulatory requirements.
Remember, data security is not a one-time effort; it requires ongoing vigilance and continuous improvement. Keep abreast of industry trends, emerging threats, and best practices to equip your organization for the challenges ahead. Embrace a culture of security, and you’ll not only protect your valuable data but also build customer trust and bolster your reputation in the market.
In an increasingly interconnected world, prioritizing data security in your SaaS operations is not just a smart business decision—it’s an essential one. With the right strategies and expertise, you can navigate the complexities of data protection and emerge stronger and more resilient than ever.


